Our Security Approach
AppDeck is in active development. We are building the platform with security-first architecture from day one — here is how, and which certifications we do not yet hold.
Where We Are Today
AppDeck is pre-launch. We are not currently holding SOC 2, ISO 27001, or HIPAA certifications — these require production systems, real customer data, and third-party audits we have not yet completed. We believe being transparent about this matters more than marketing language suggests otherwise.
If you are evaluating AppDeck and have specific security, compliance, or residency requirements, tell us in your demo request and we will walk through exactly what we support today and what is on the near-term roadmap.
Compliance Status
Where AppDeck stands on common privacy and compliance frameworks:
- GDPR: Our data handling design follows GDPR principles — lawful basis, data minimization, right to access and deletion, and breach notification. We will sign a DPA with customers in scope.
- HIPAA: Not currently in scope. If you have PHI workloads, let us know and we can discuss timeline.
Access Controls & Authentication
The platform is being built with granular access control as a first-class feature:
- Role-Based Access Control (RBAC): Custom roles and permissions so users only see what their role requires.
- Single Sign-On (SSO): Planned support for SAML-based identity providers (Okta, Azure AD, Google Workspace). Not yet generally available — ask about timeline in your demo request.
Infrastructure Security
AppDeck is hosted on mainstream cloud infrastructure. Our general approach:
- Cloud Environment: Hosted on a mainstream cloud provider.
- Network Security: We rely on the network-level protections our cloud provider offers.
- Vulnerability Management: We work to keep software dependencies up to date, and we plan to add independent security review ahead of general availability.
- Backup and Recovery: We are putting backup and recovery procedures in place as the platform moves toward launch.
Data Privacy
We are committed to handling your data transparently. Our current practices are outlined in our Privacy Policy; we will update it as the product matures and will notify customers of material changes.
Read Our Privacy PolicyIncident Response
We are documenting an incident response process covering detection, containment, customer notification, and post-incident review. Early-access customers will receive the current version of this document on request.
Questions About Security?
If you are evaluating AppDeck and have specific security or compliance requirements, tell us what you need. We will answer honestly about what is in place today and what is on the roadmap.
Contact UsRelated Articles
Learn more about this topic from our expert guides and resources.
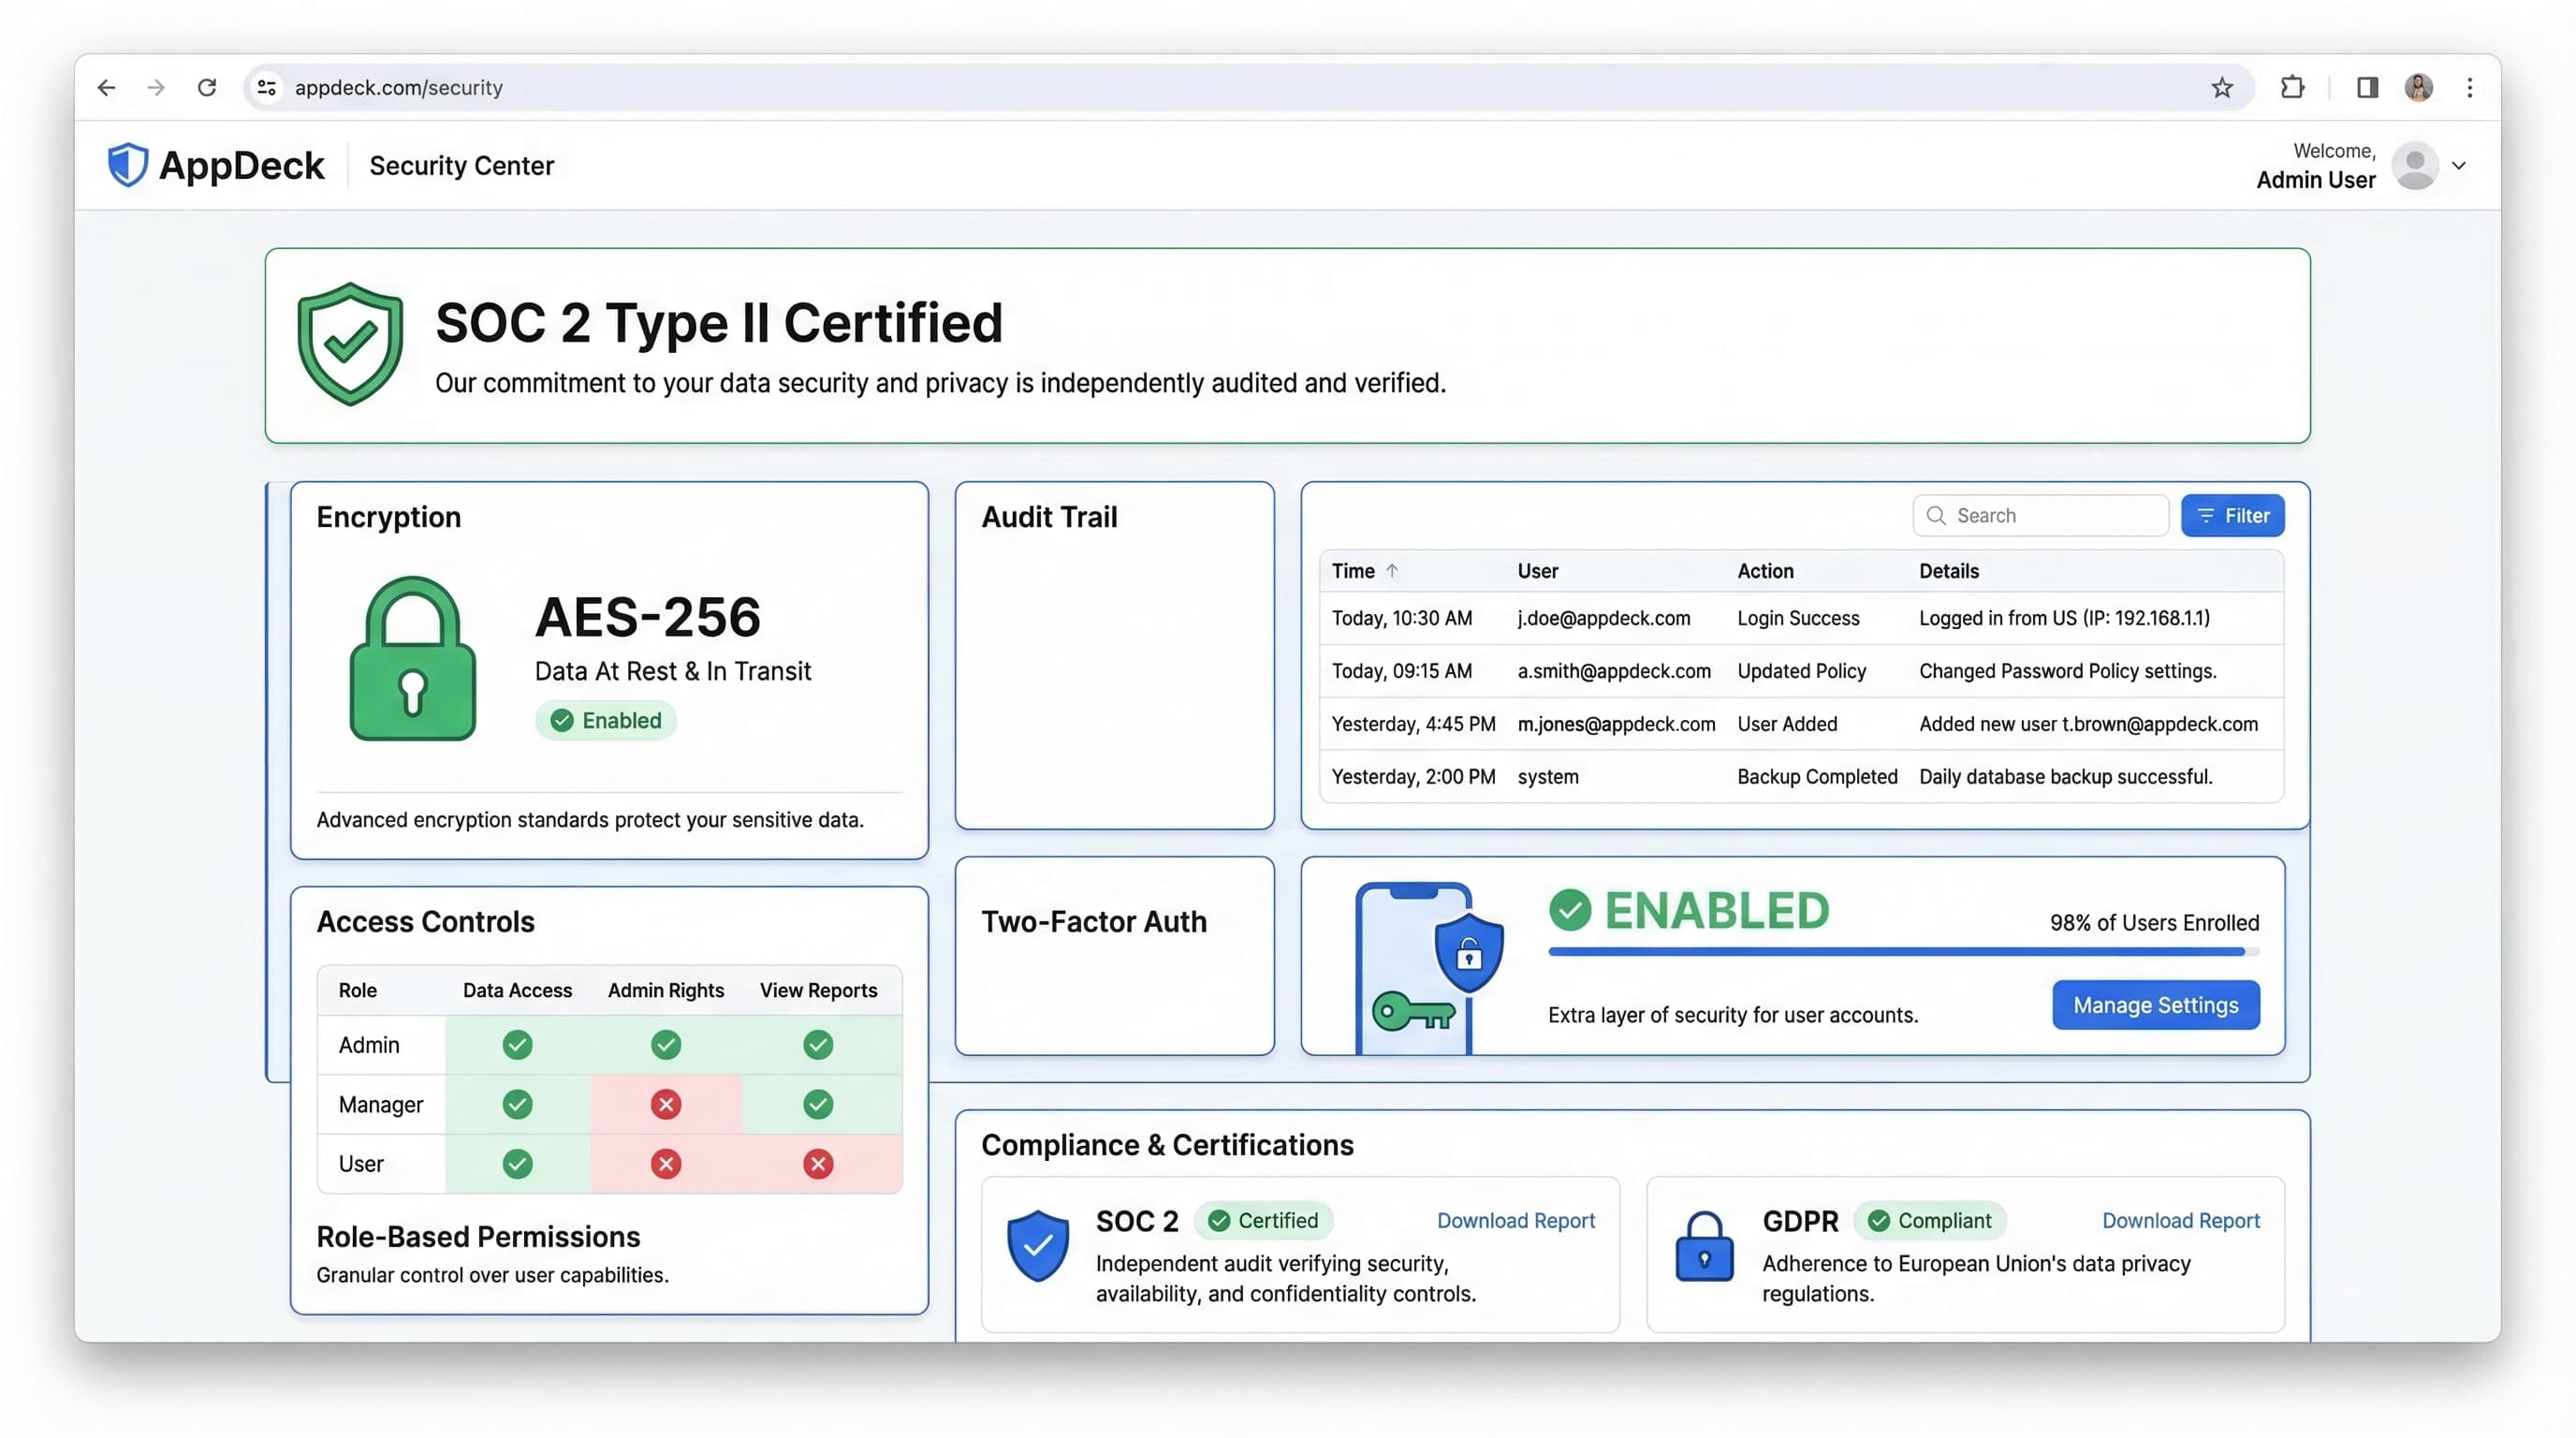
Secure Board Portal: Complete Security Checklist for Board Communications
Essential security checklist for board portal software. Covers encryption, access controls, compliance (SOC 2, GDPR), audit trails, and vendor security assessment.
Read Article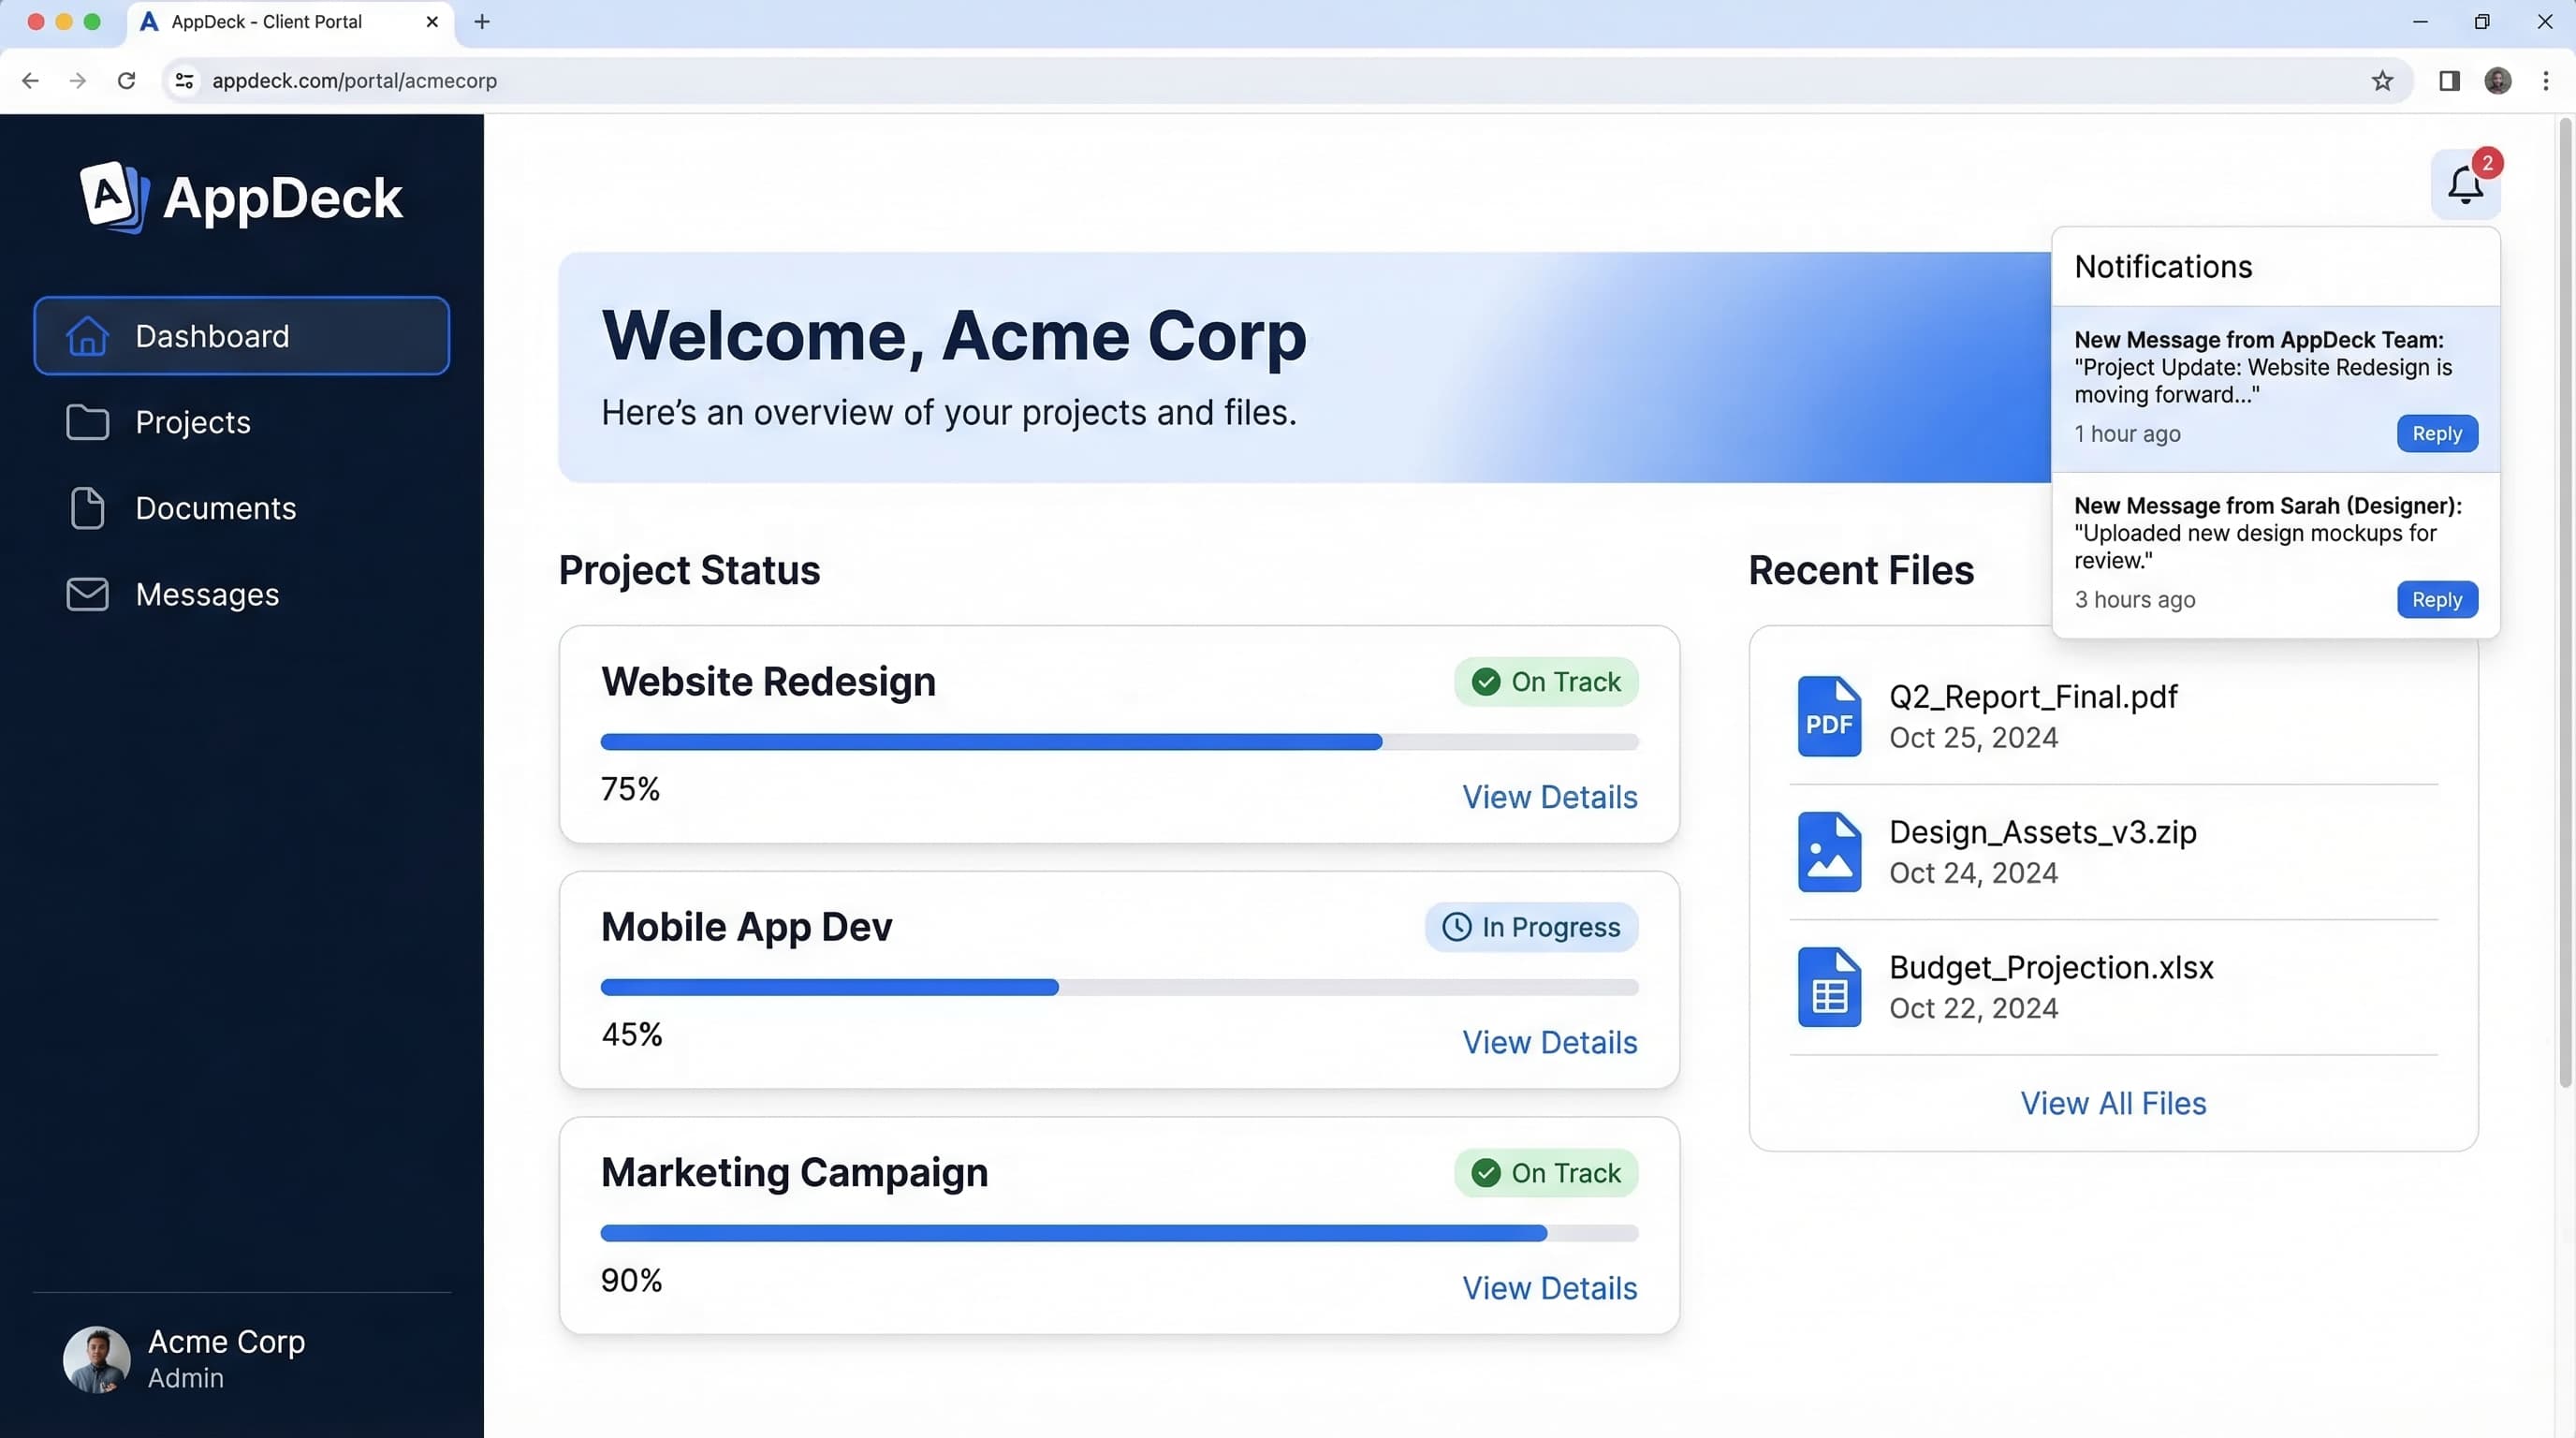
Secure Client Portal: The Complete Security Guide for Professional Services
How to build a secure client portal. SOC 2, encryption, access controls, HIPAA compliance, and security checklist for agencies and law firms.
Read Article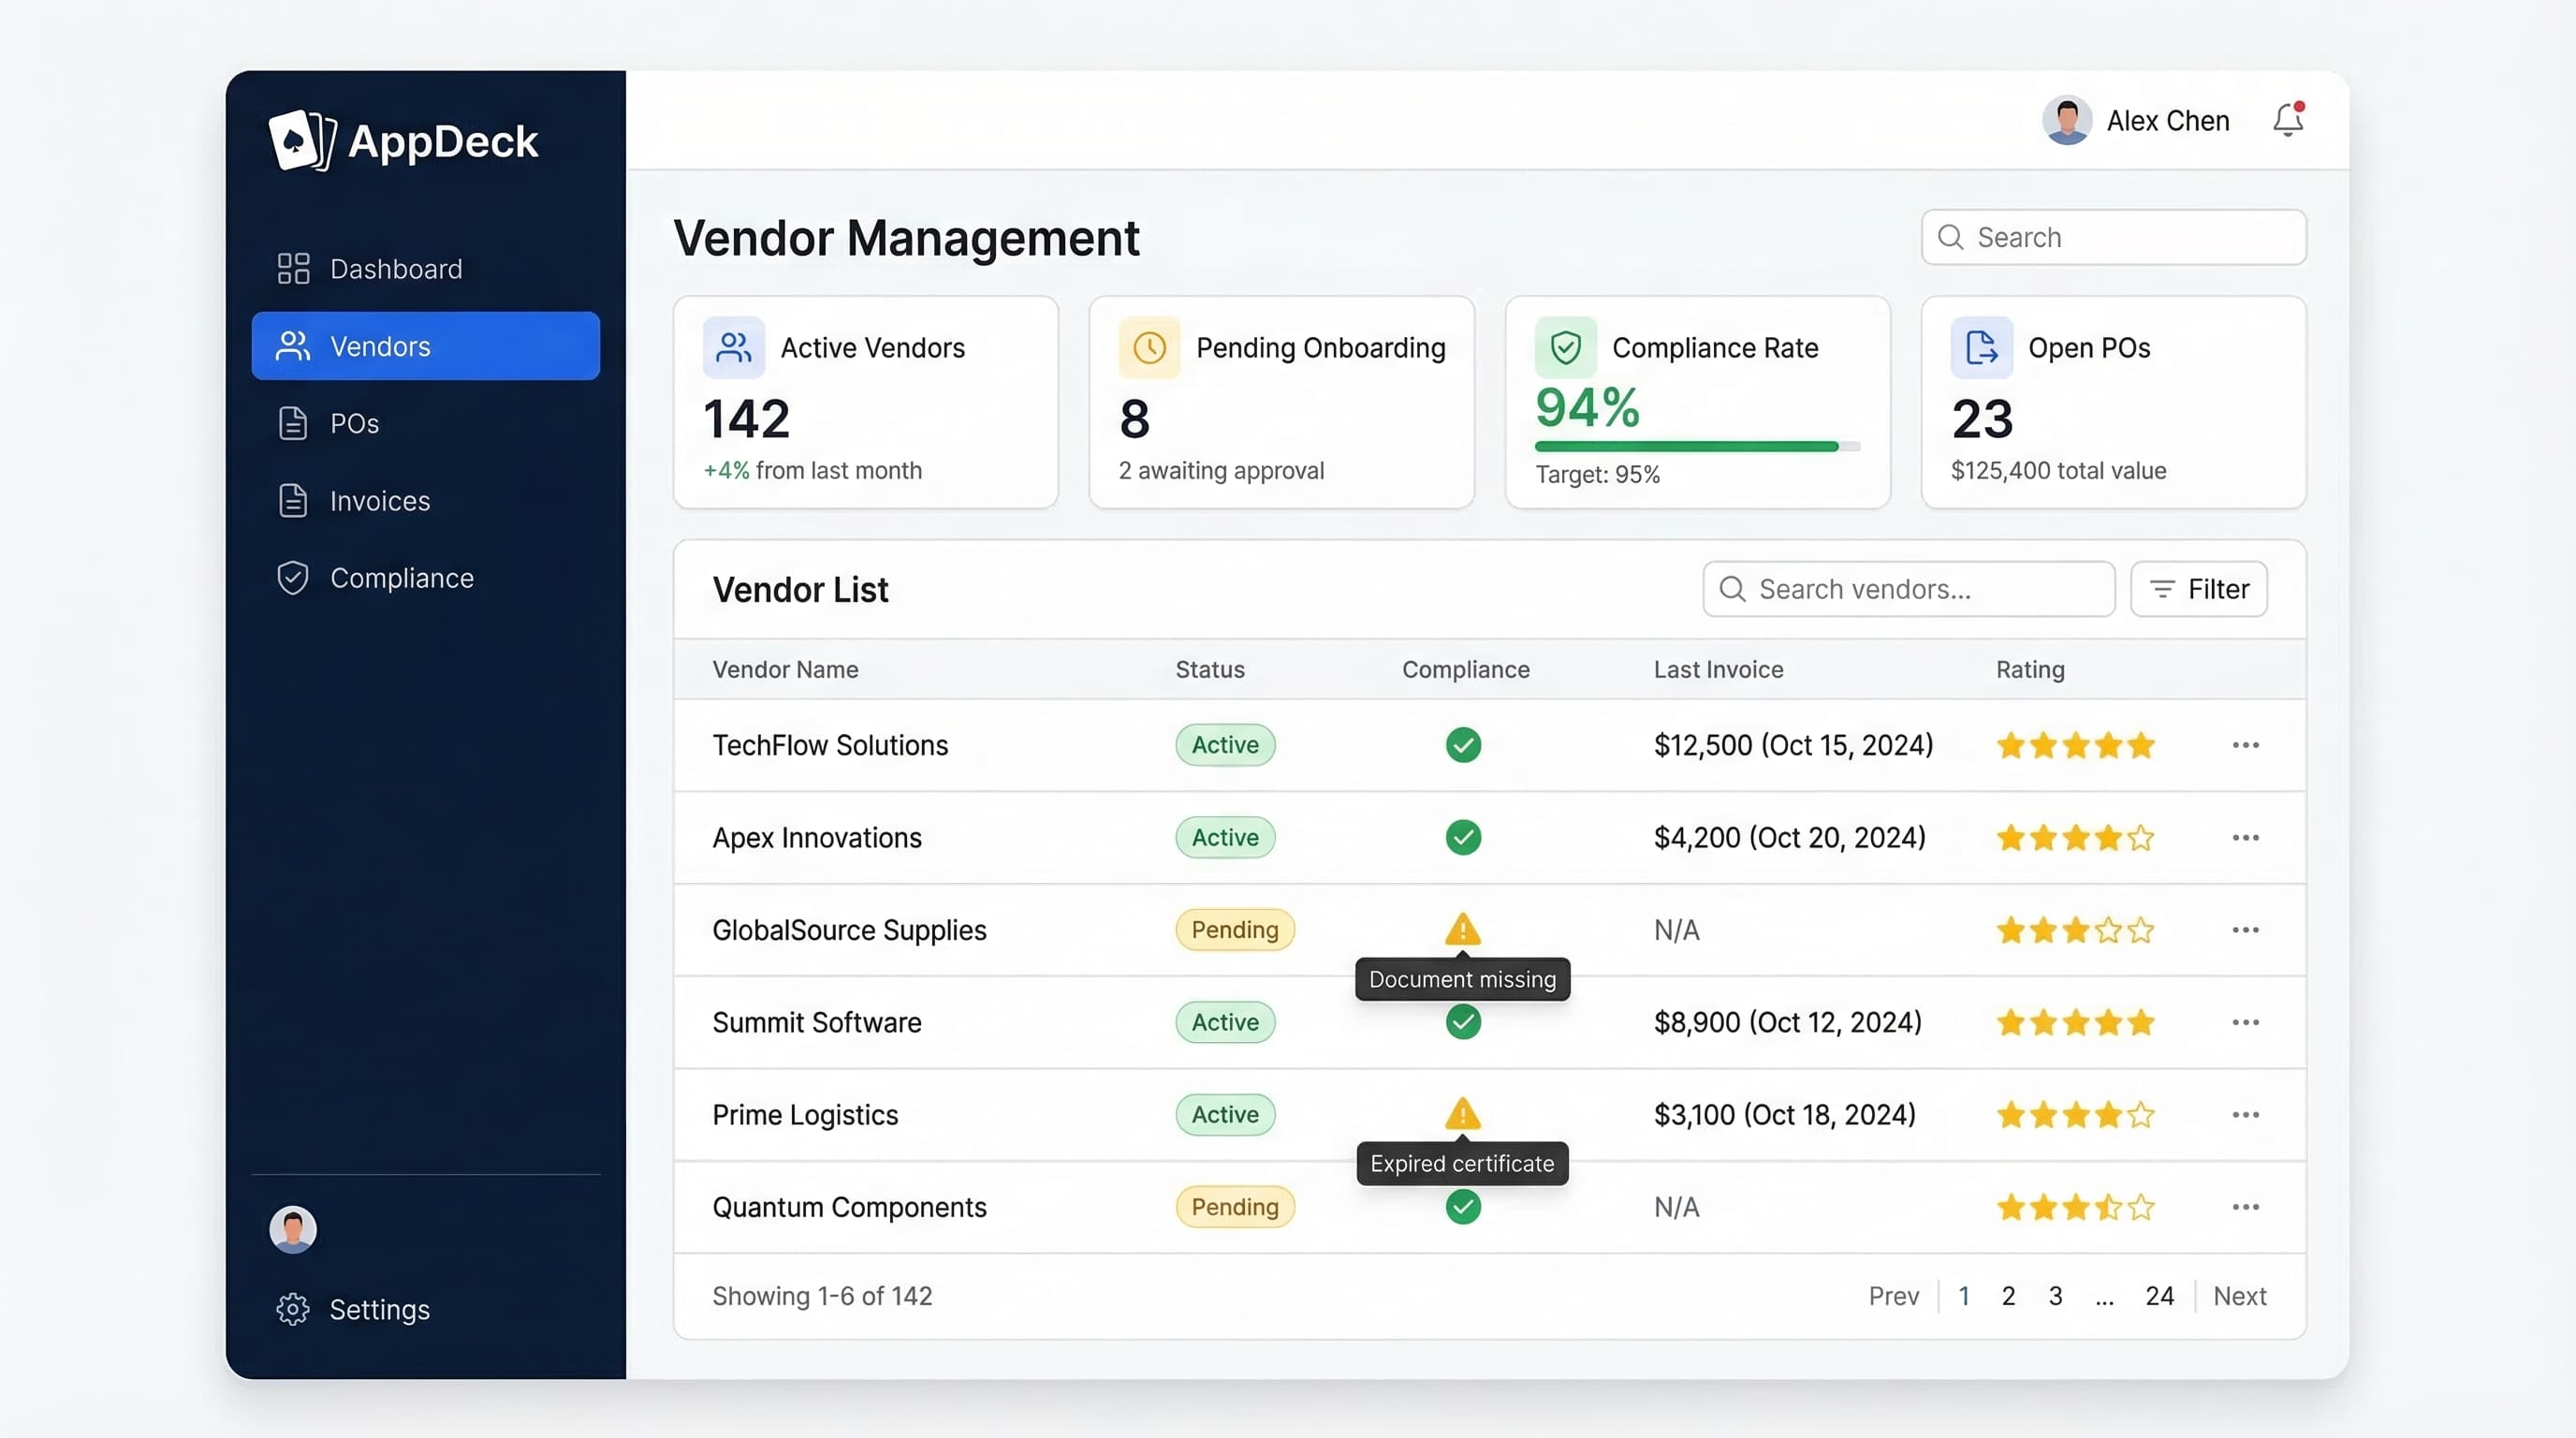
Vendor Compliance Checklist: 30 Items Every Procurement Team Needs
Complete vendor compliance checklist for procurement teams. Track certifications, insurance, licenses, contracts, and regulatory requirements with automated reminders.
Read Article